Understand the dependency
Identify relevant suppliers, services, information access and the owners of those relationships.
Third-party risk management
Identify the third parties in scope and establish how supplier risks, due diligence and outstanding actions should be managed.
Discuss your requirementsTHE WORK INVOLVED
Identify relevant suppliers, services, information access and the owners of those relationships.
Agree what should be reviewed, from contractual responsibilities to available assurance evidence.
Relate findings to your organisation’s risk approach and record decisions with accountable owners.
Agree follow-up actions and a practical process for reassessing supplier relationships.
CONNECTED WORKSPACE
Use the implementation workflow to connect supplier review actions with the wider security programme. The pictured view shows the implementation workspace, not an automated supplier-monitoring product.
Discuss scope and pricing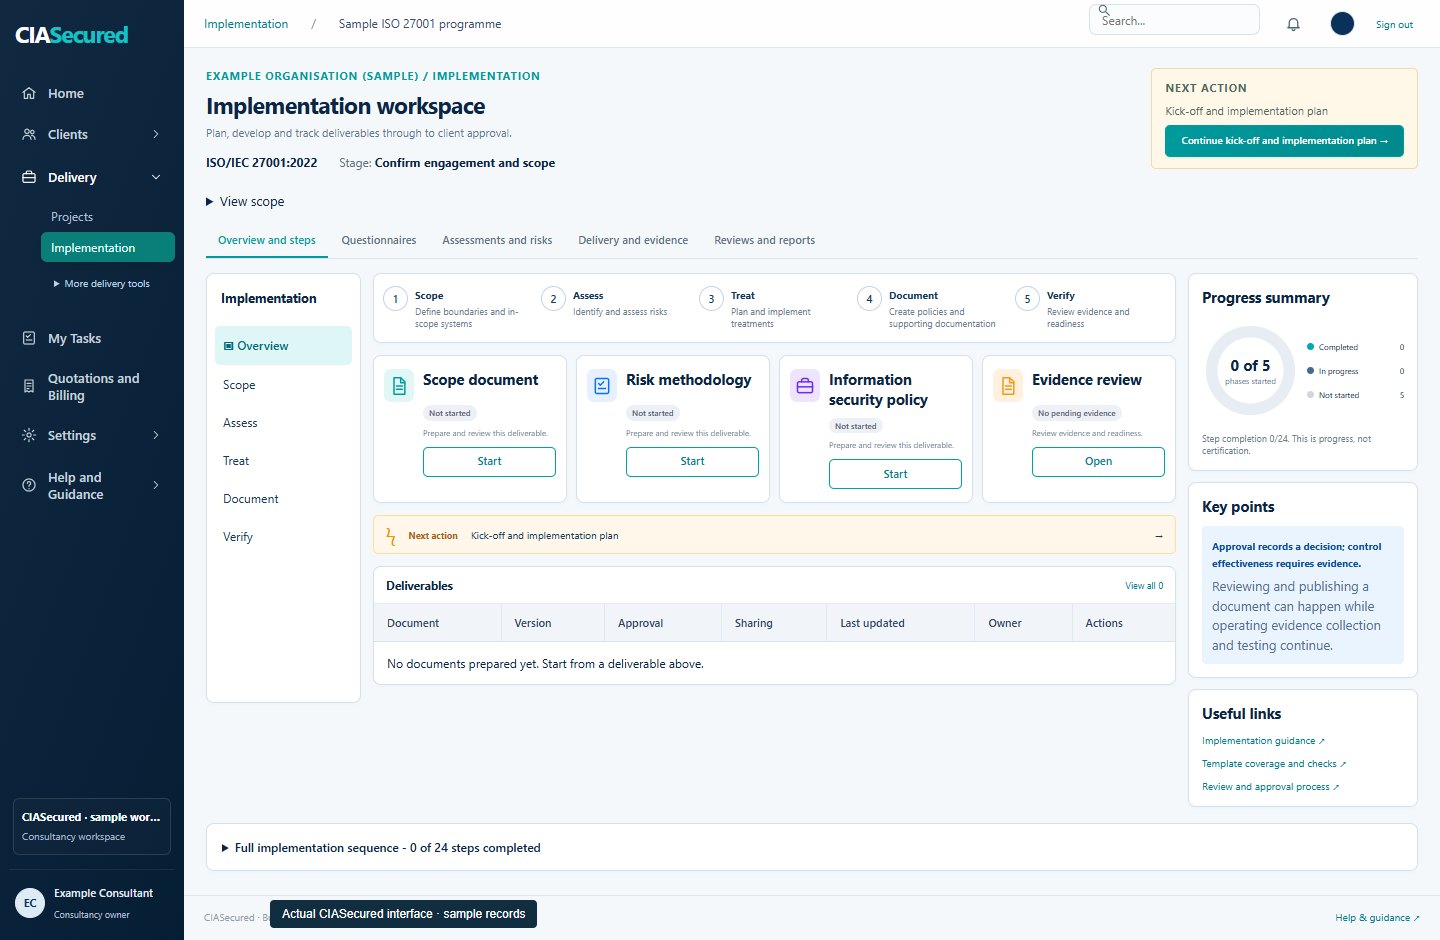
Scope, deliverables, review arrangements and external dependencies are agreed before work begins. Independent certification and third-party fees are separate unless expressly included.
WORK WITH CIASECURED
Tell us where you are now and what you need to achieve. We’ll talk through how we can help.